PlexTrac by Brinqa
One System of Record for the Offensive-Security Lifecycle
The PlexTrac by Brinqa solution
PlexTrac by Brinqa: Consistency and Insight Above the Offensive-Testing Ecosystem
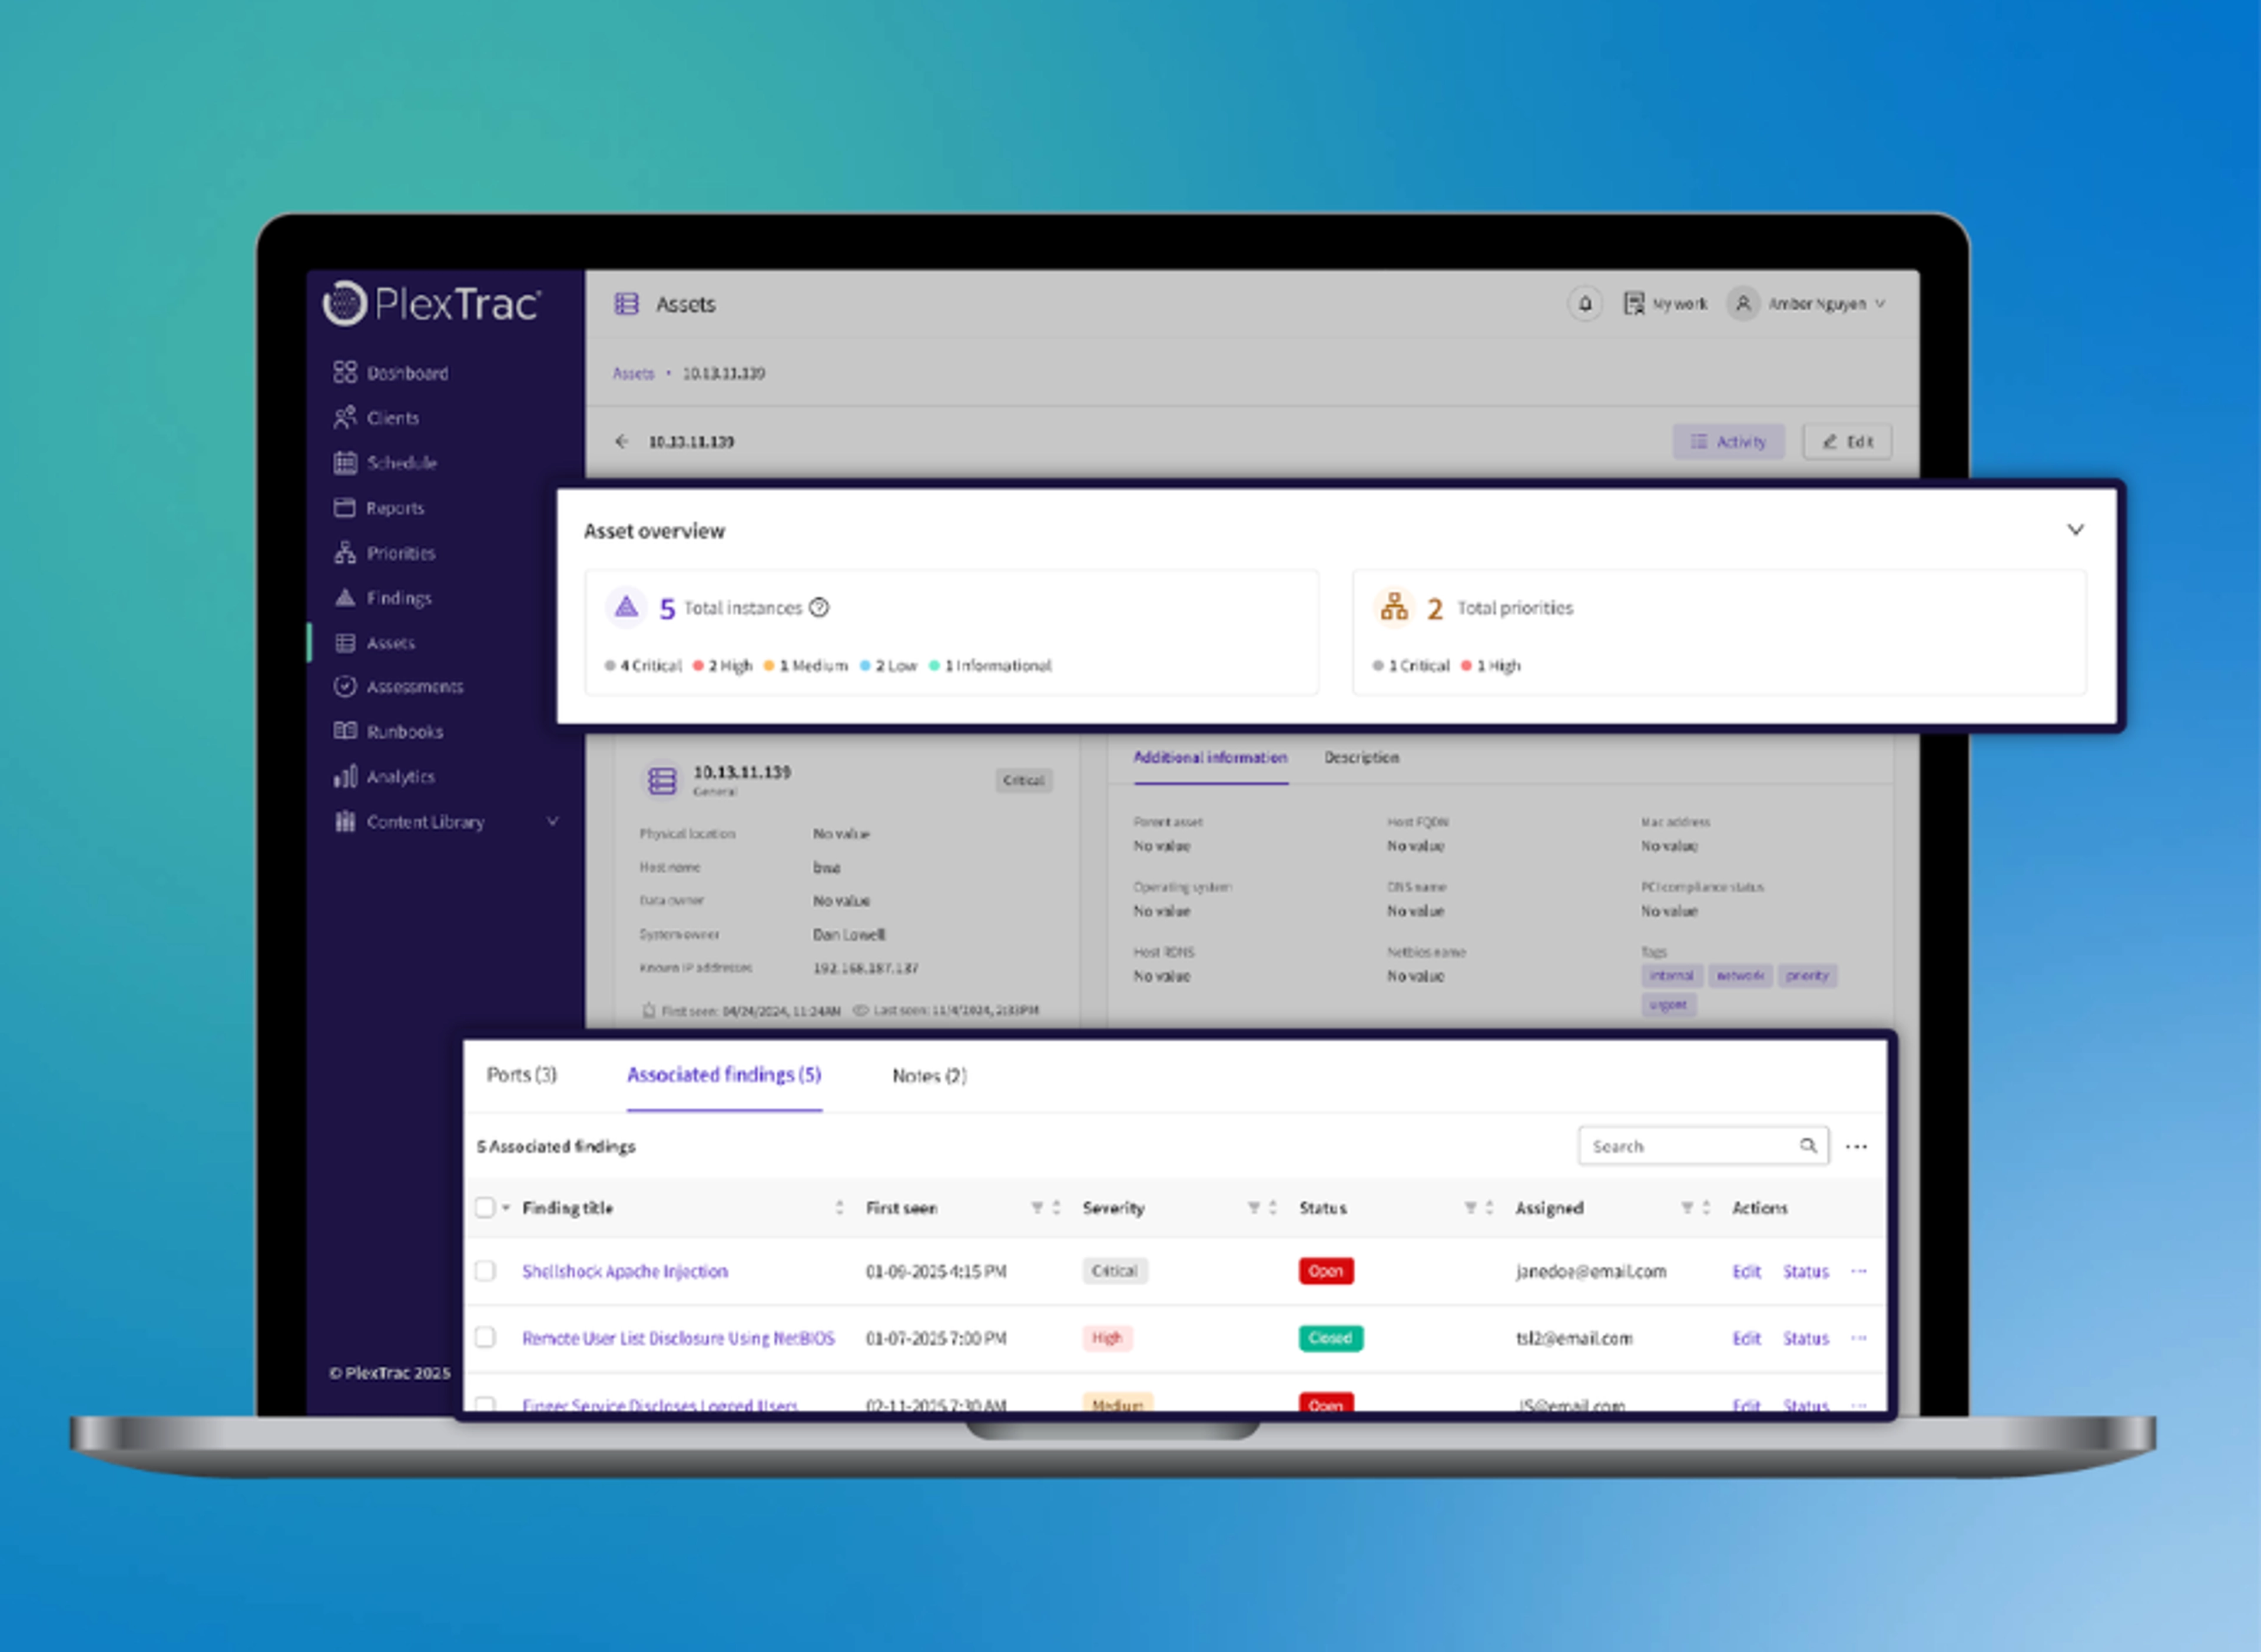
Bring every offensive-security tool into one system of record
Pen testing platforms, red team and adversary emulation exercises, and retest evidence all live in one place instead of scattered across tools.
✓ Problems solved:
- Siloed data. Results from every offensive-security tool and workflow come together in one platform.
- Lost validation evidence. Retest results stay attached to the original finding, wherever they were captured.
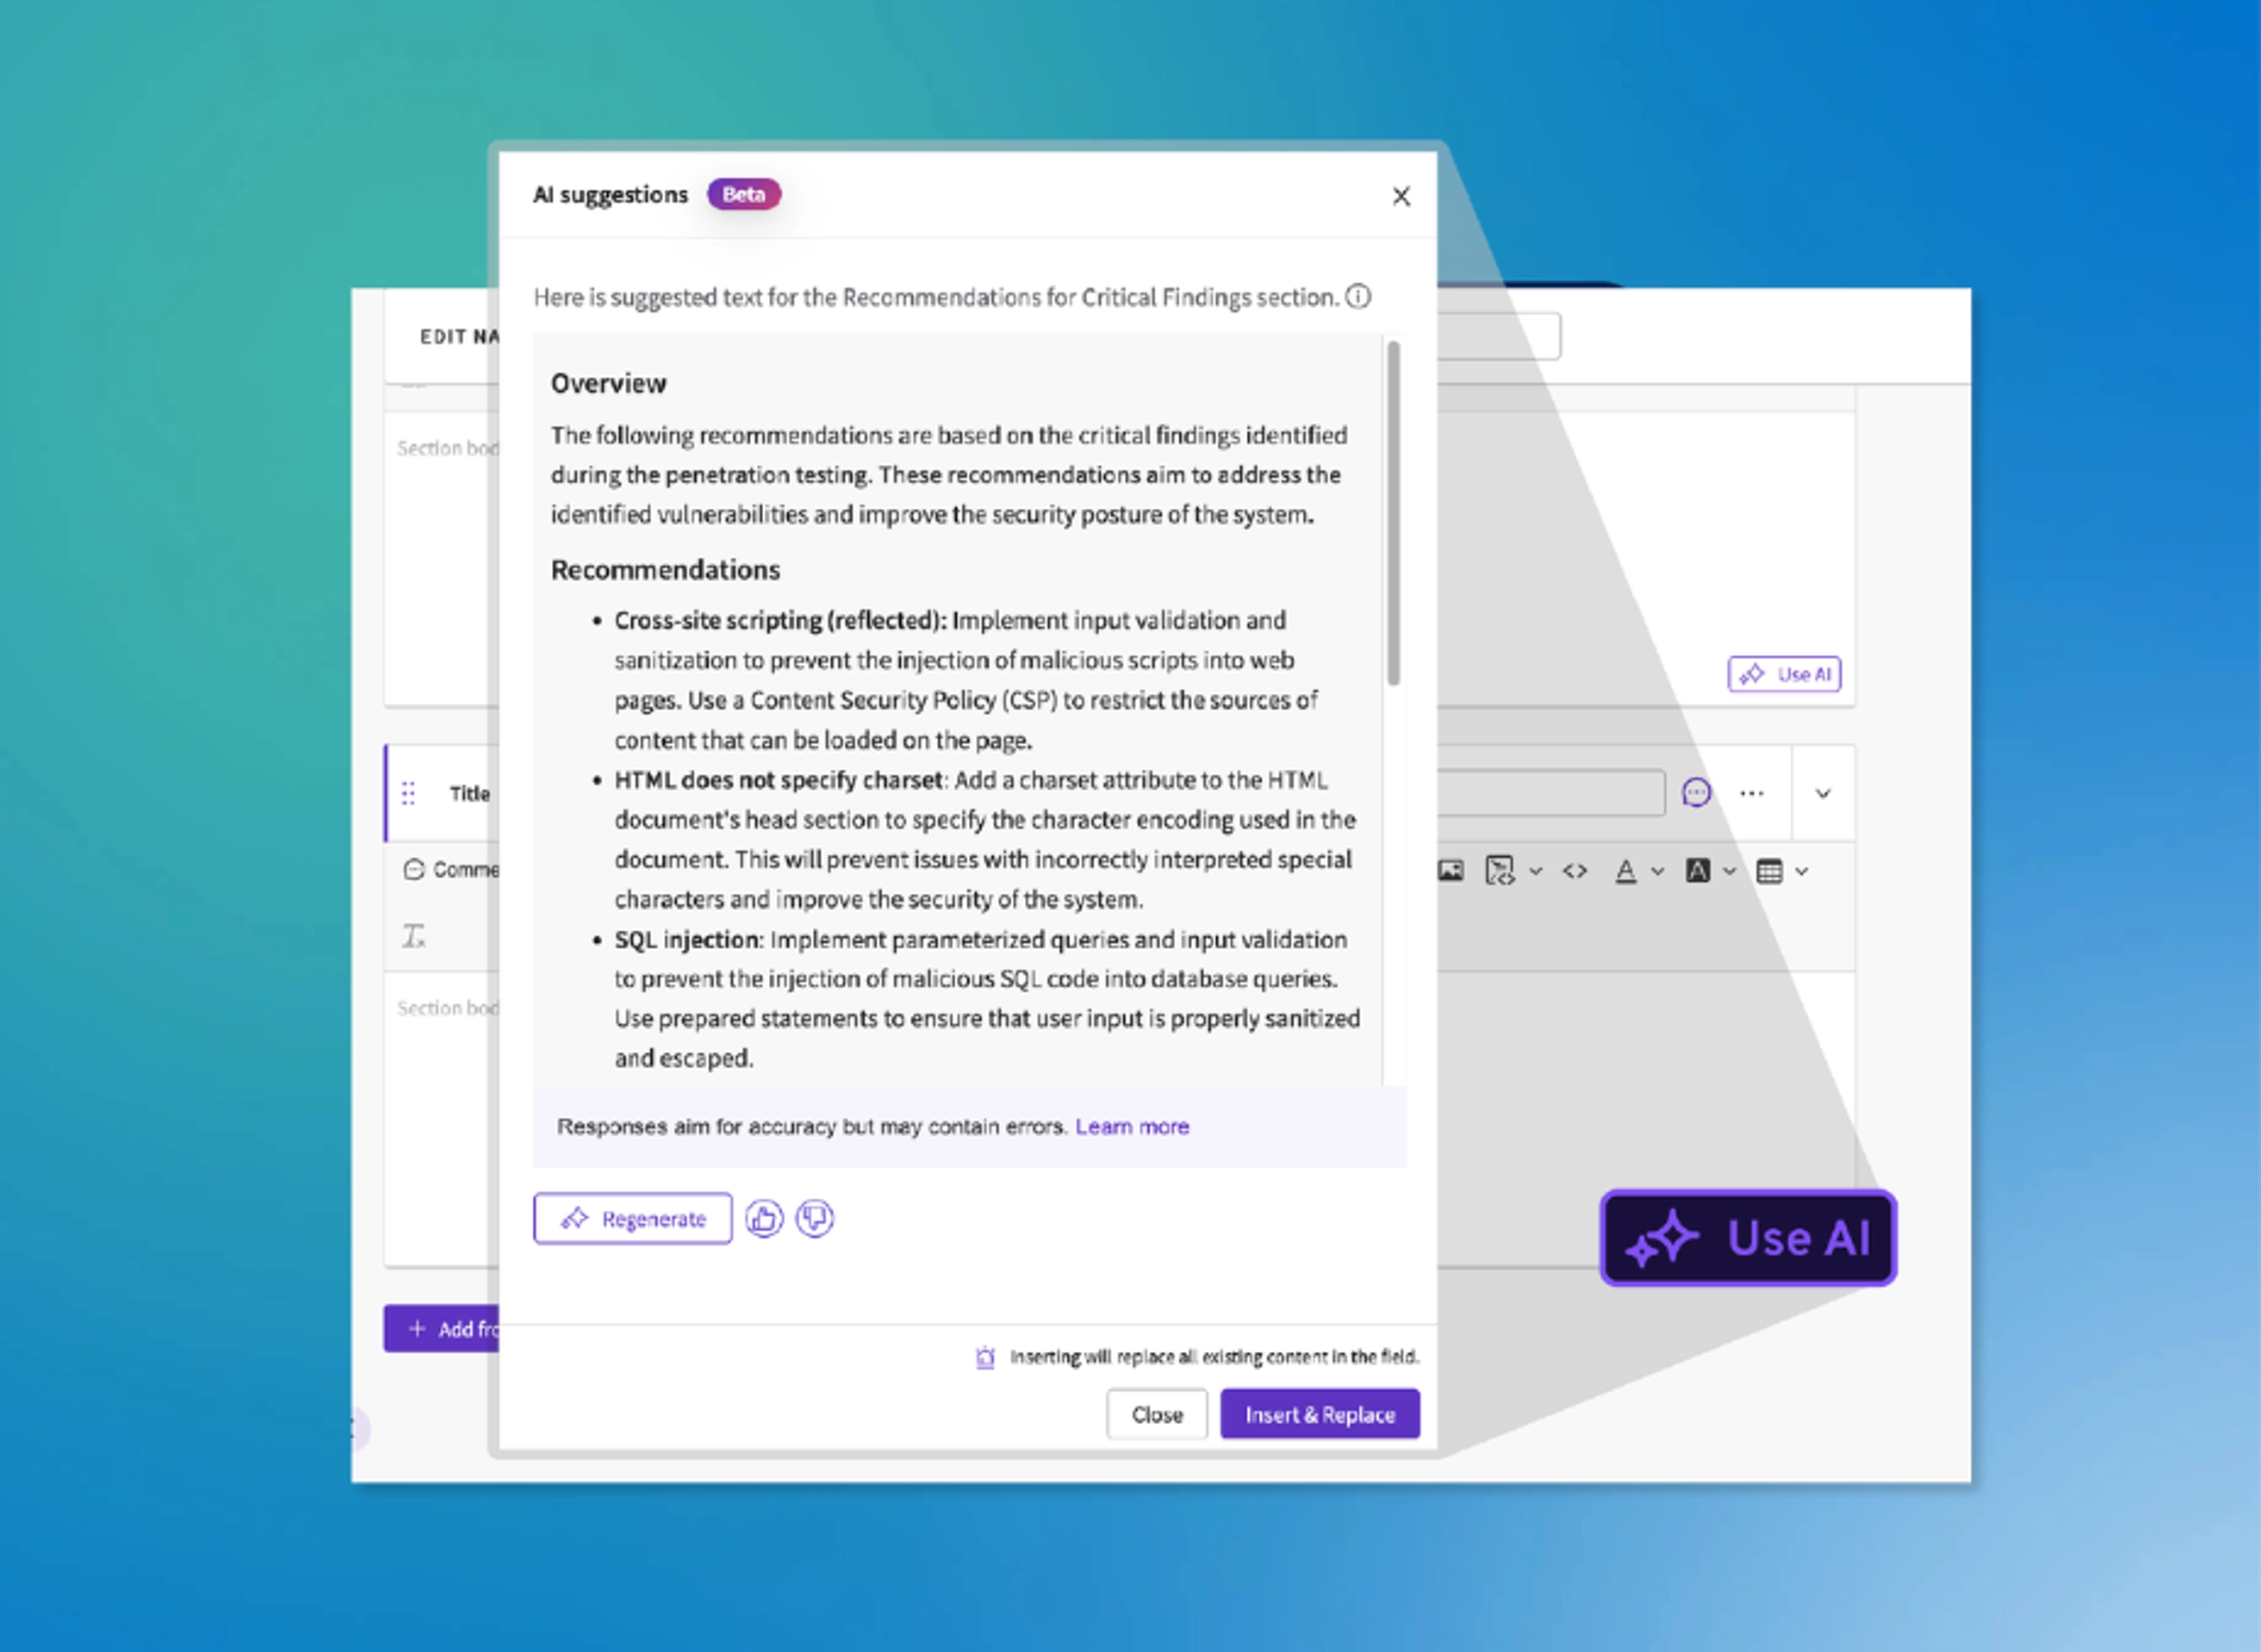
Write less, ship more
AI-assisted descriptions and remediation steps, plus 25,000+ reusable write-ups, cut first-draft time dramatically.
✓ Problems solved:
- Reporting that outlasts the testing. AI-assisted writing takes reports from first draft to final delivery in a fraction of the time.
- Every engagement starting over. Reusable write-ups and remediation language carry over from one engagement to the next.
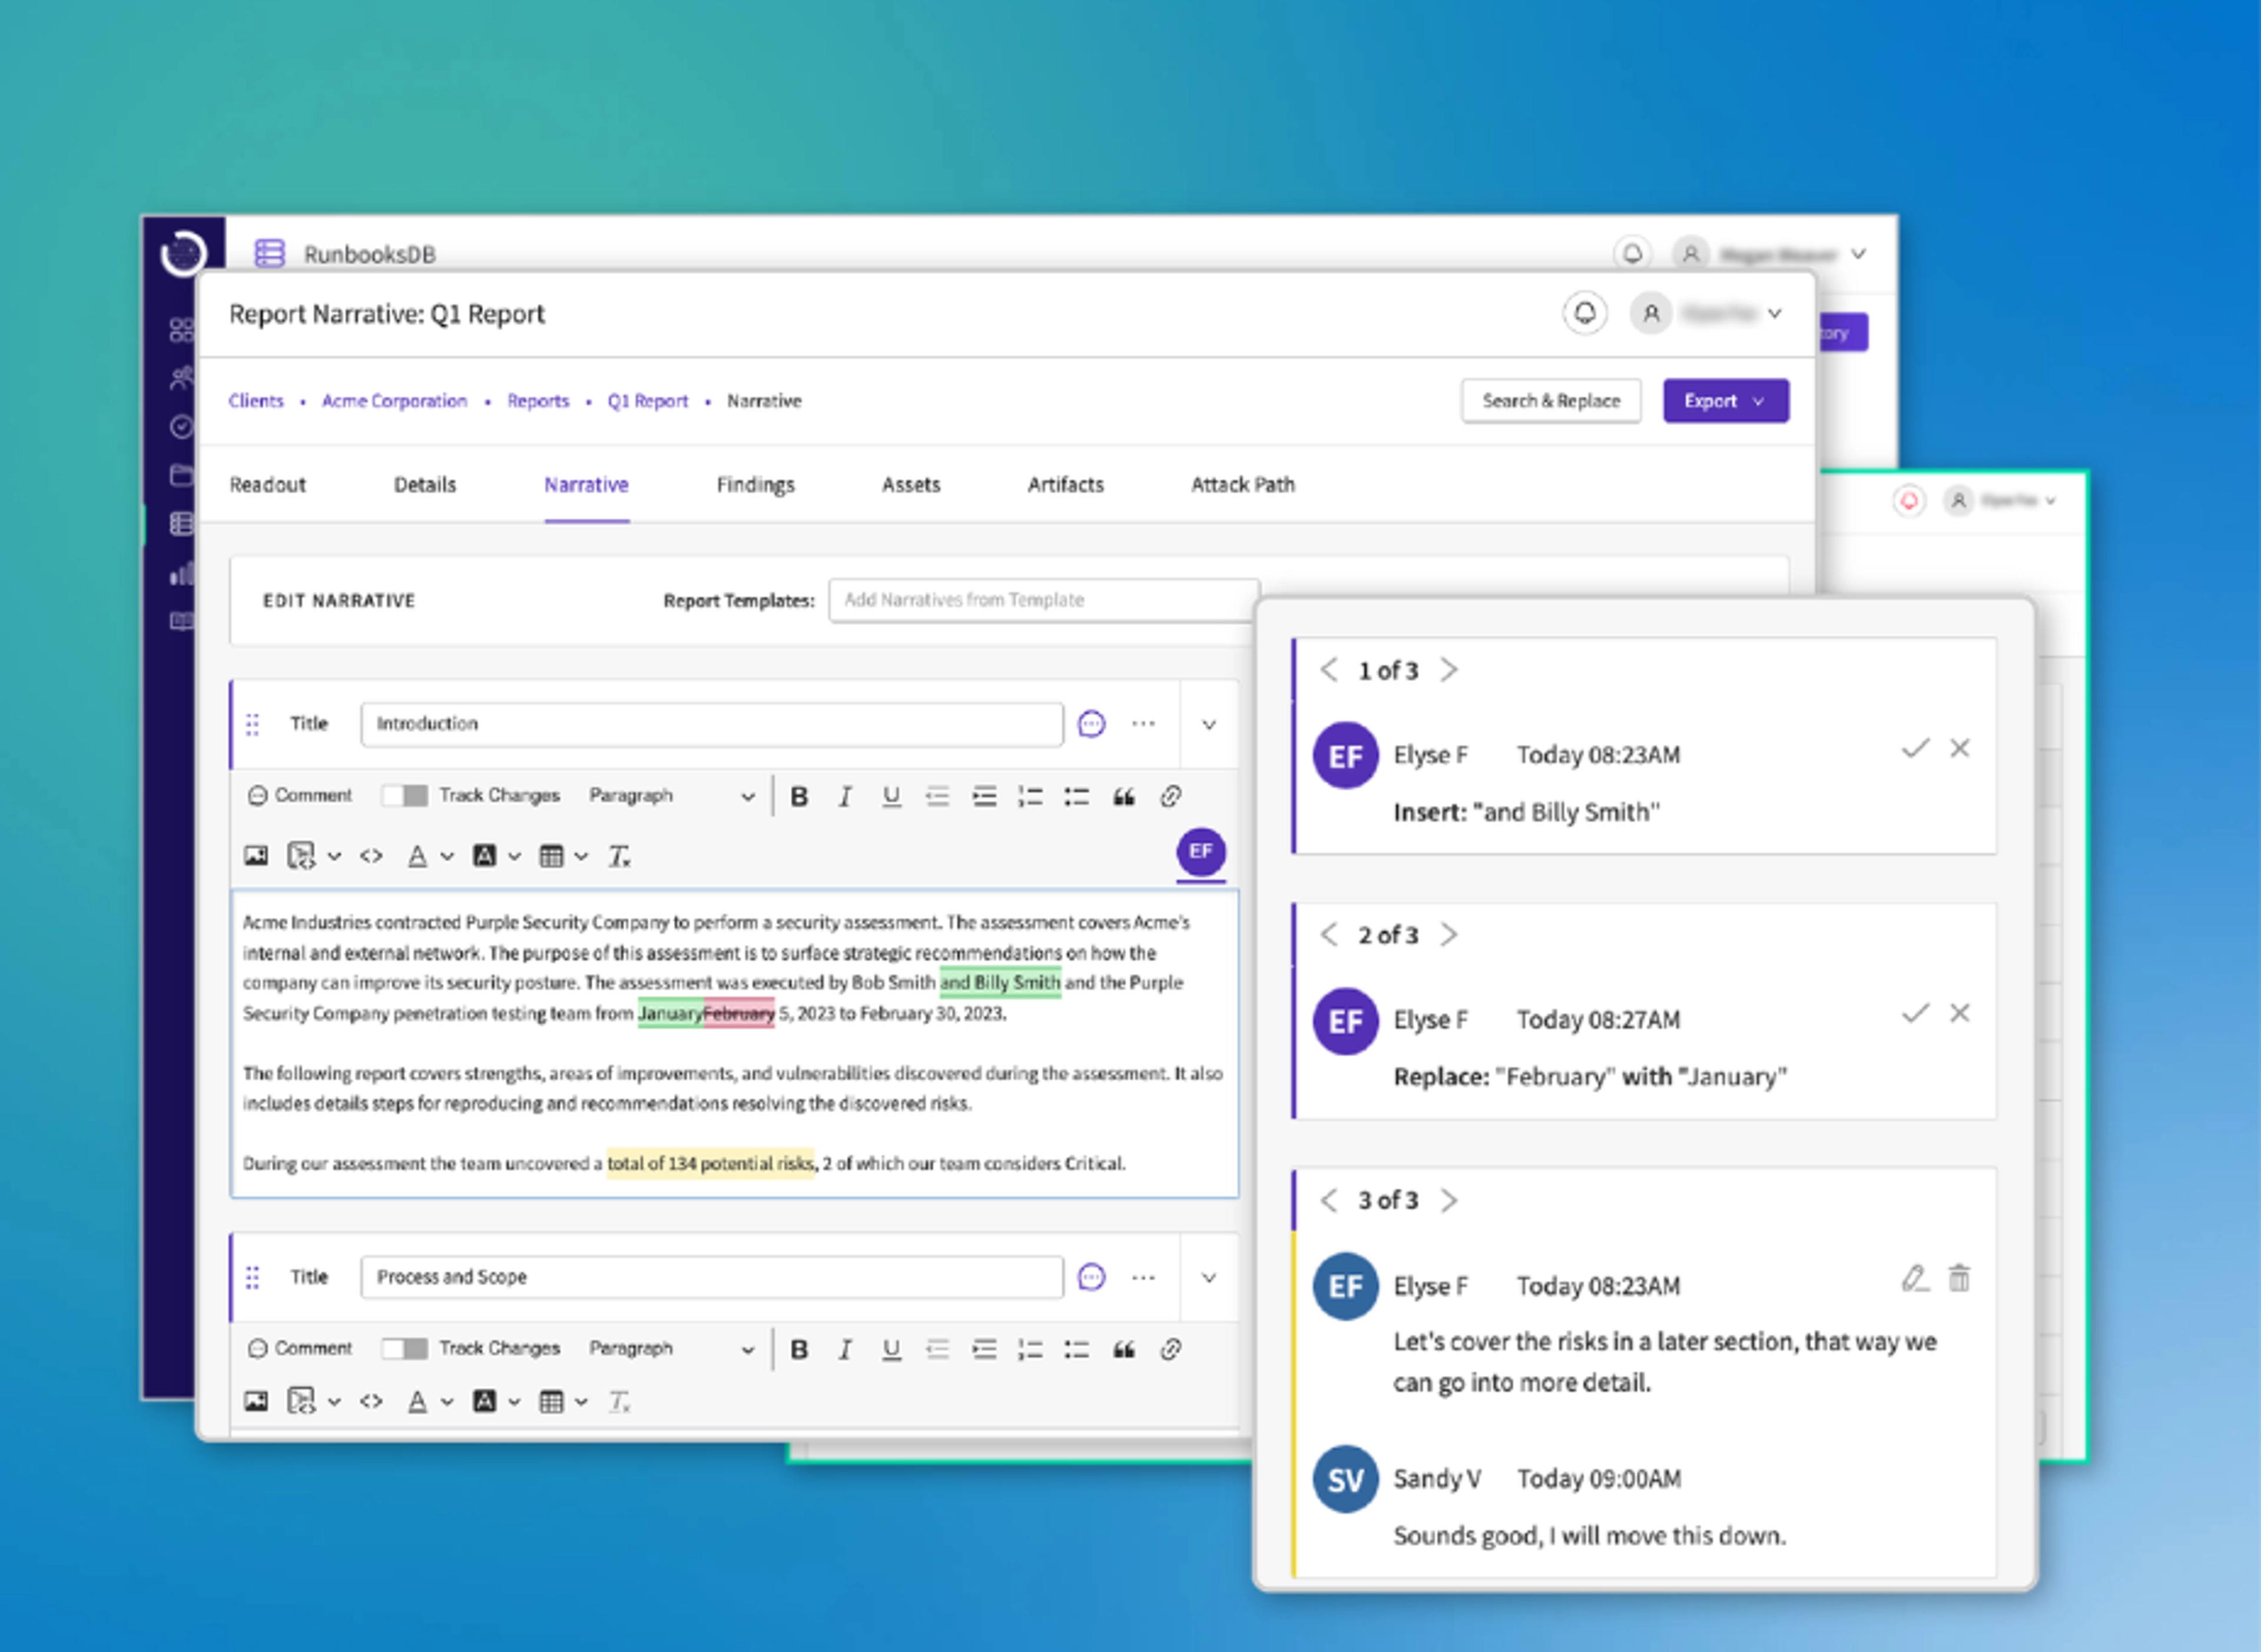
Collaborate in real time
Google-doc-style commenting and change tracking replace the email chains testers used to review a report.
✓ Problems solved:
- Slow QA between testers. Reviewers comment and track changes inside the report, so final validation happens in one place.
- Scheduling conflicts. Teams plan engagements against a shared capacity calendar.
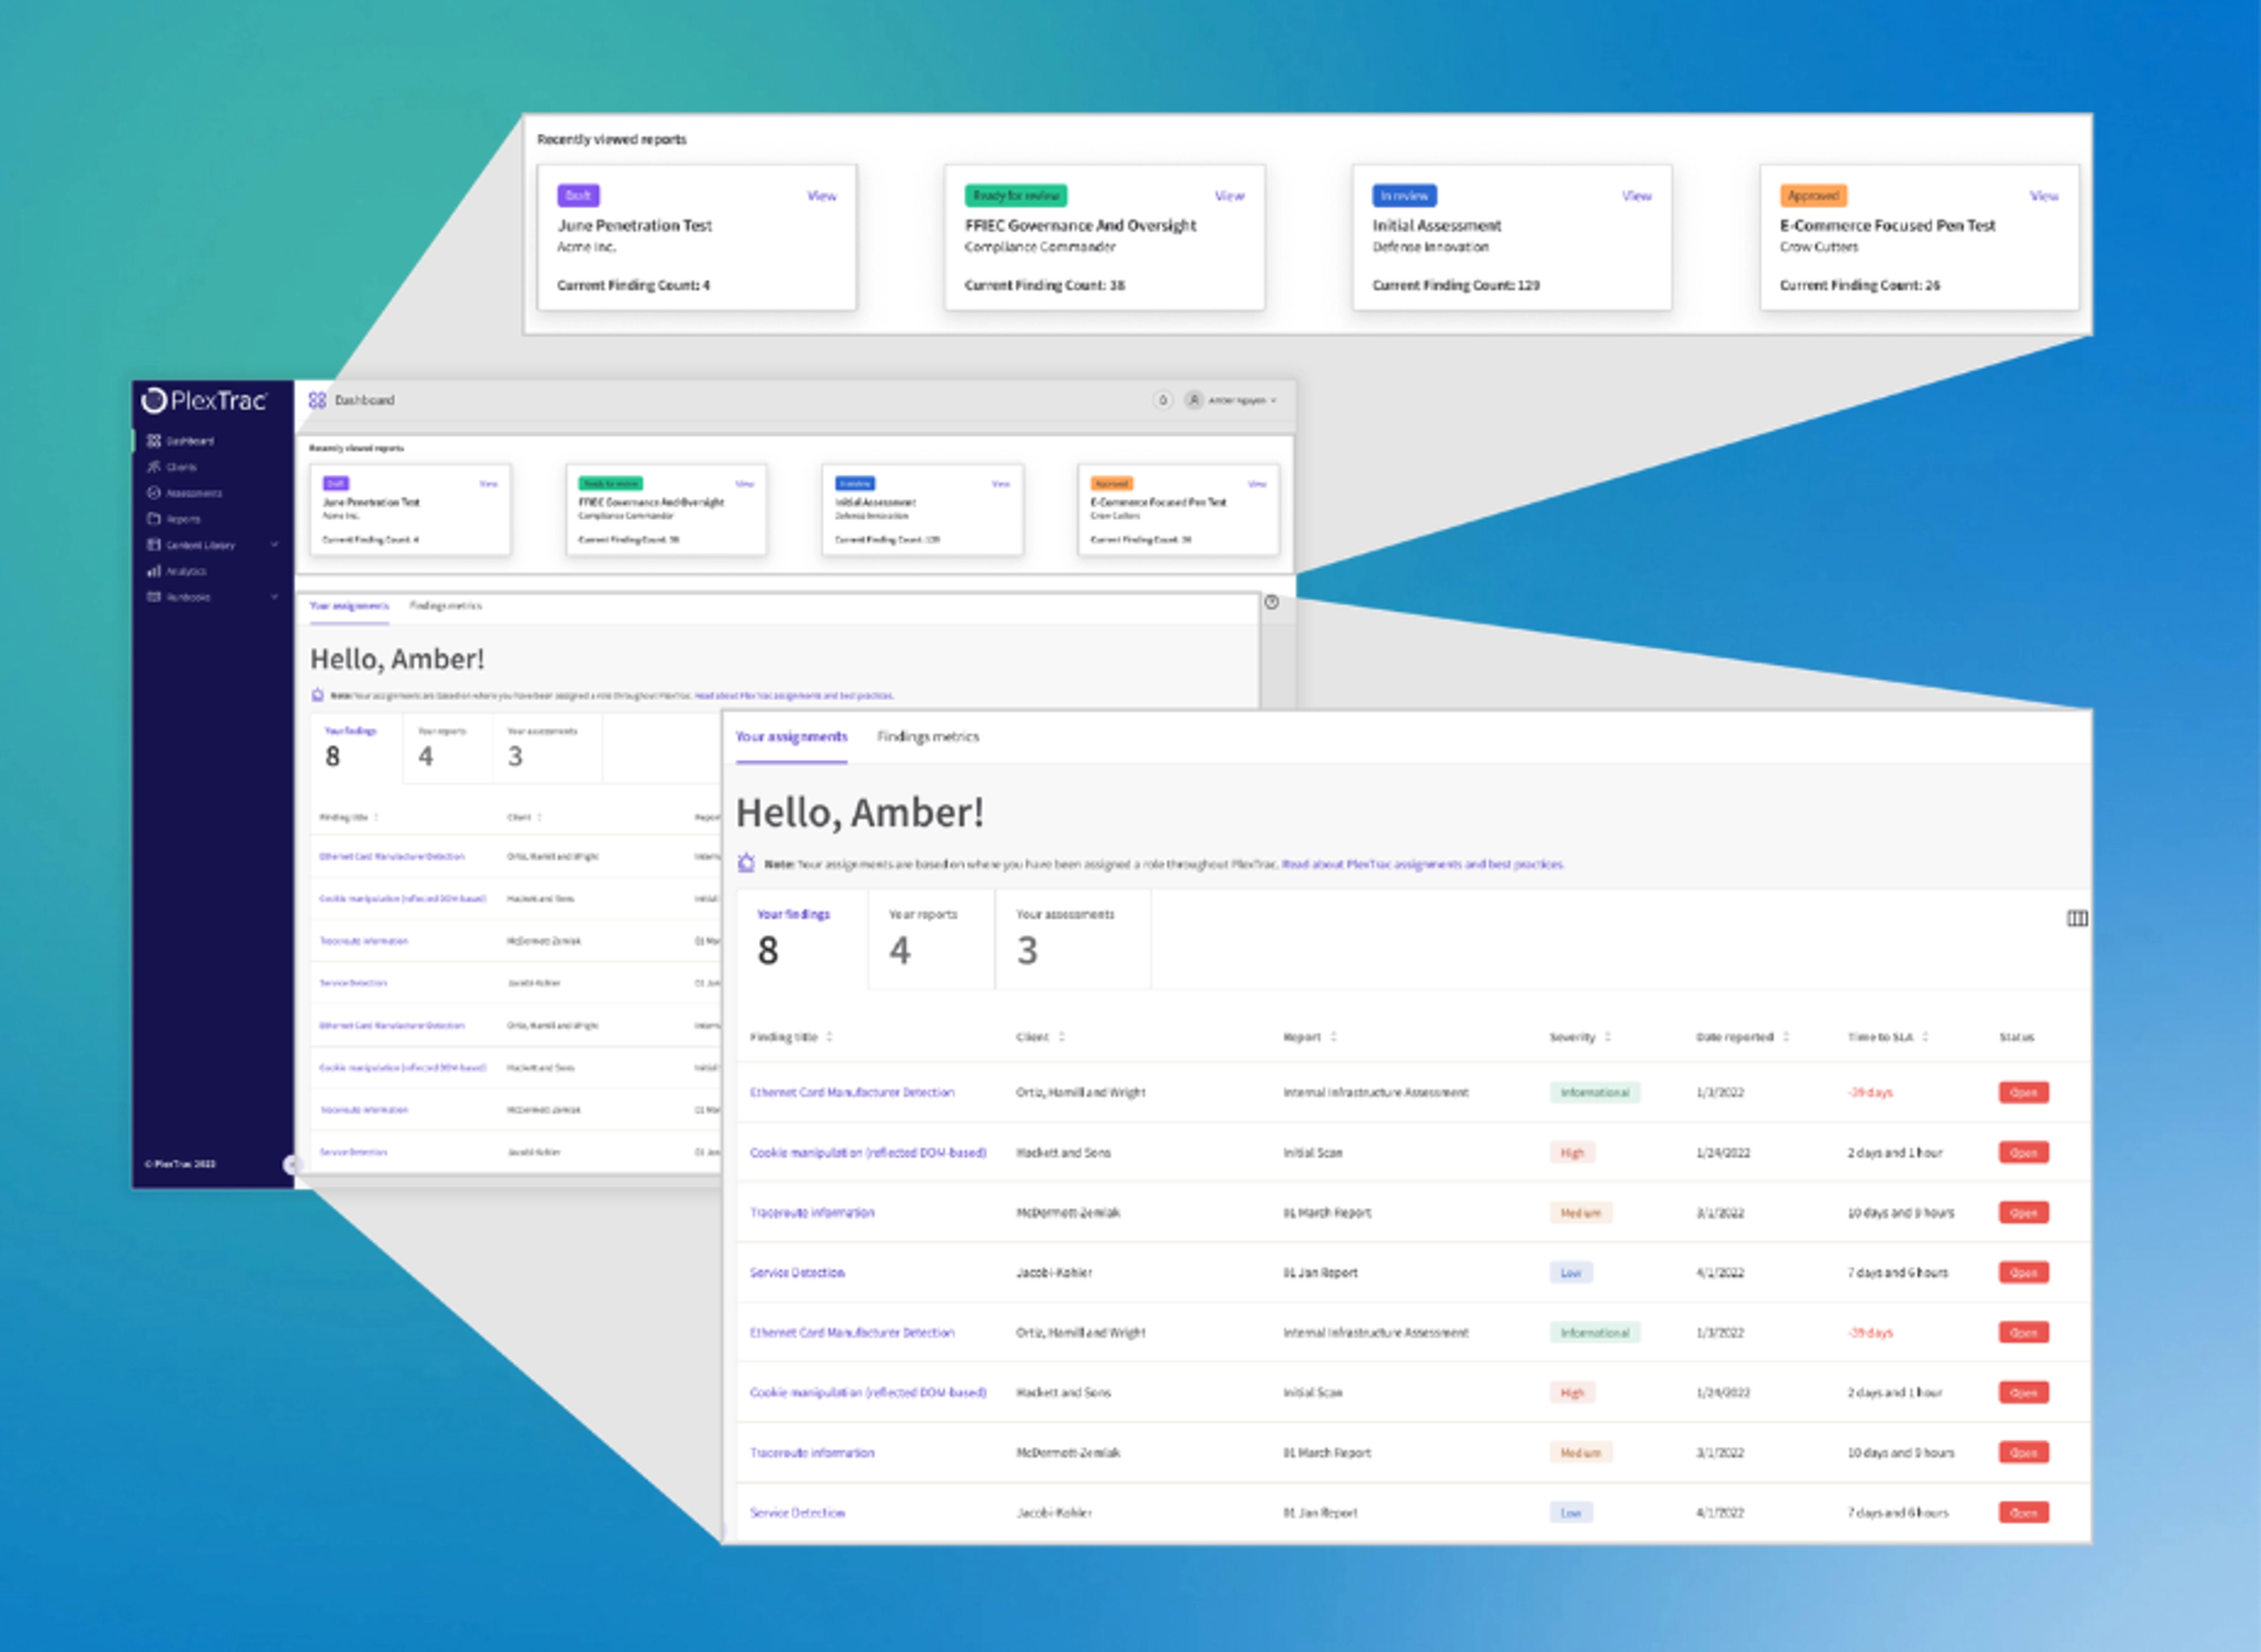
Brand every report without code
Configurable, no-code style guides put reports in the format each client expects.
✓ Problems solved:
- Quality that varies by tester. Shared style guides keep report depth and structure consistent, whoever ran the test.
- Design requests for every client. Each report comes out in the client's own branding and format automatically.
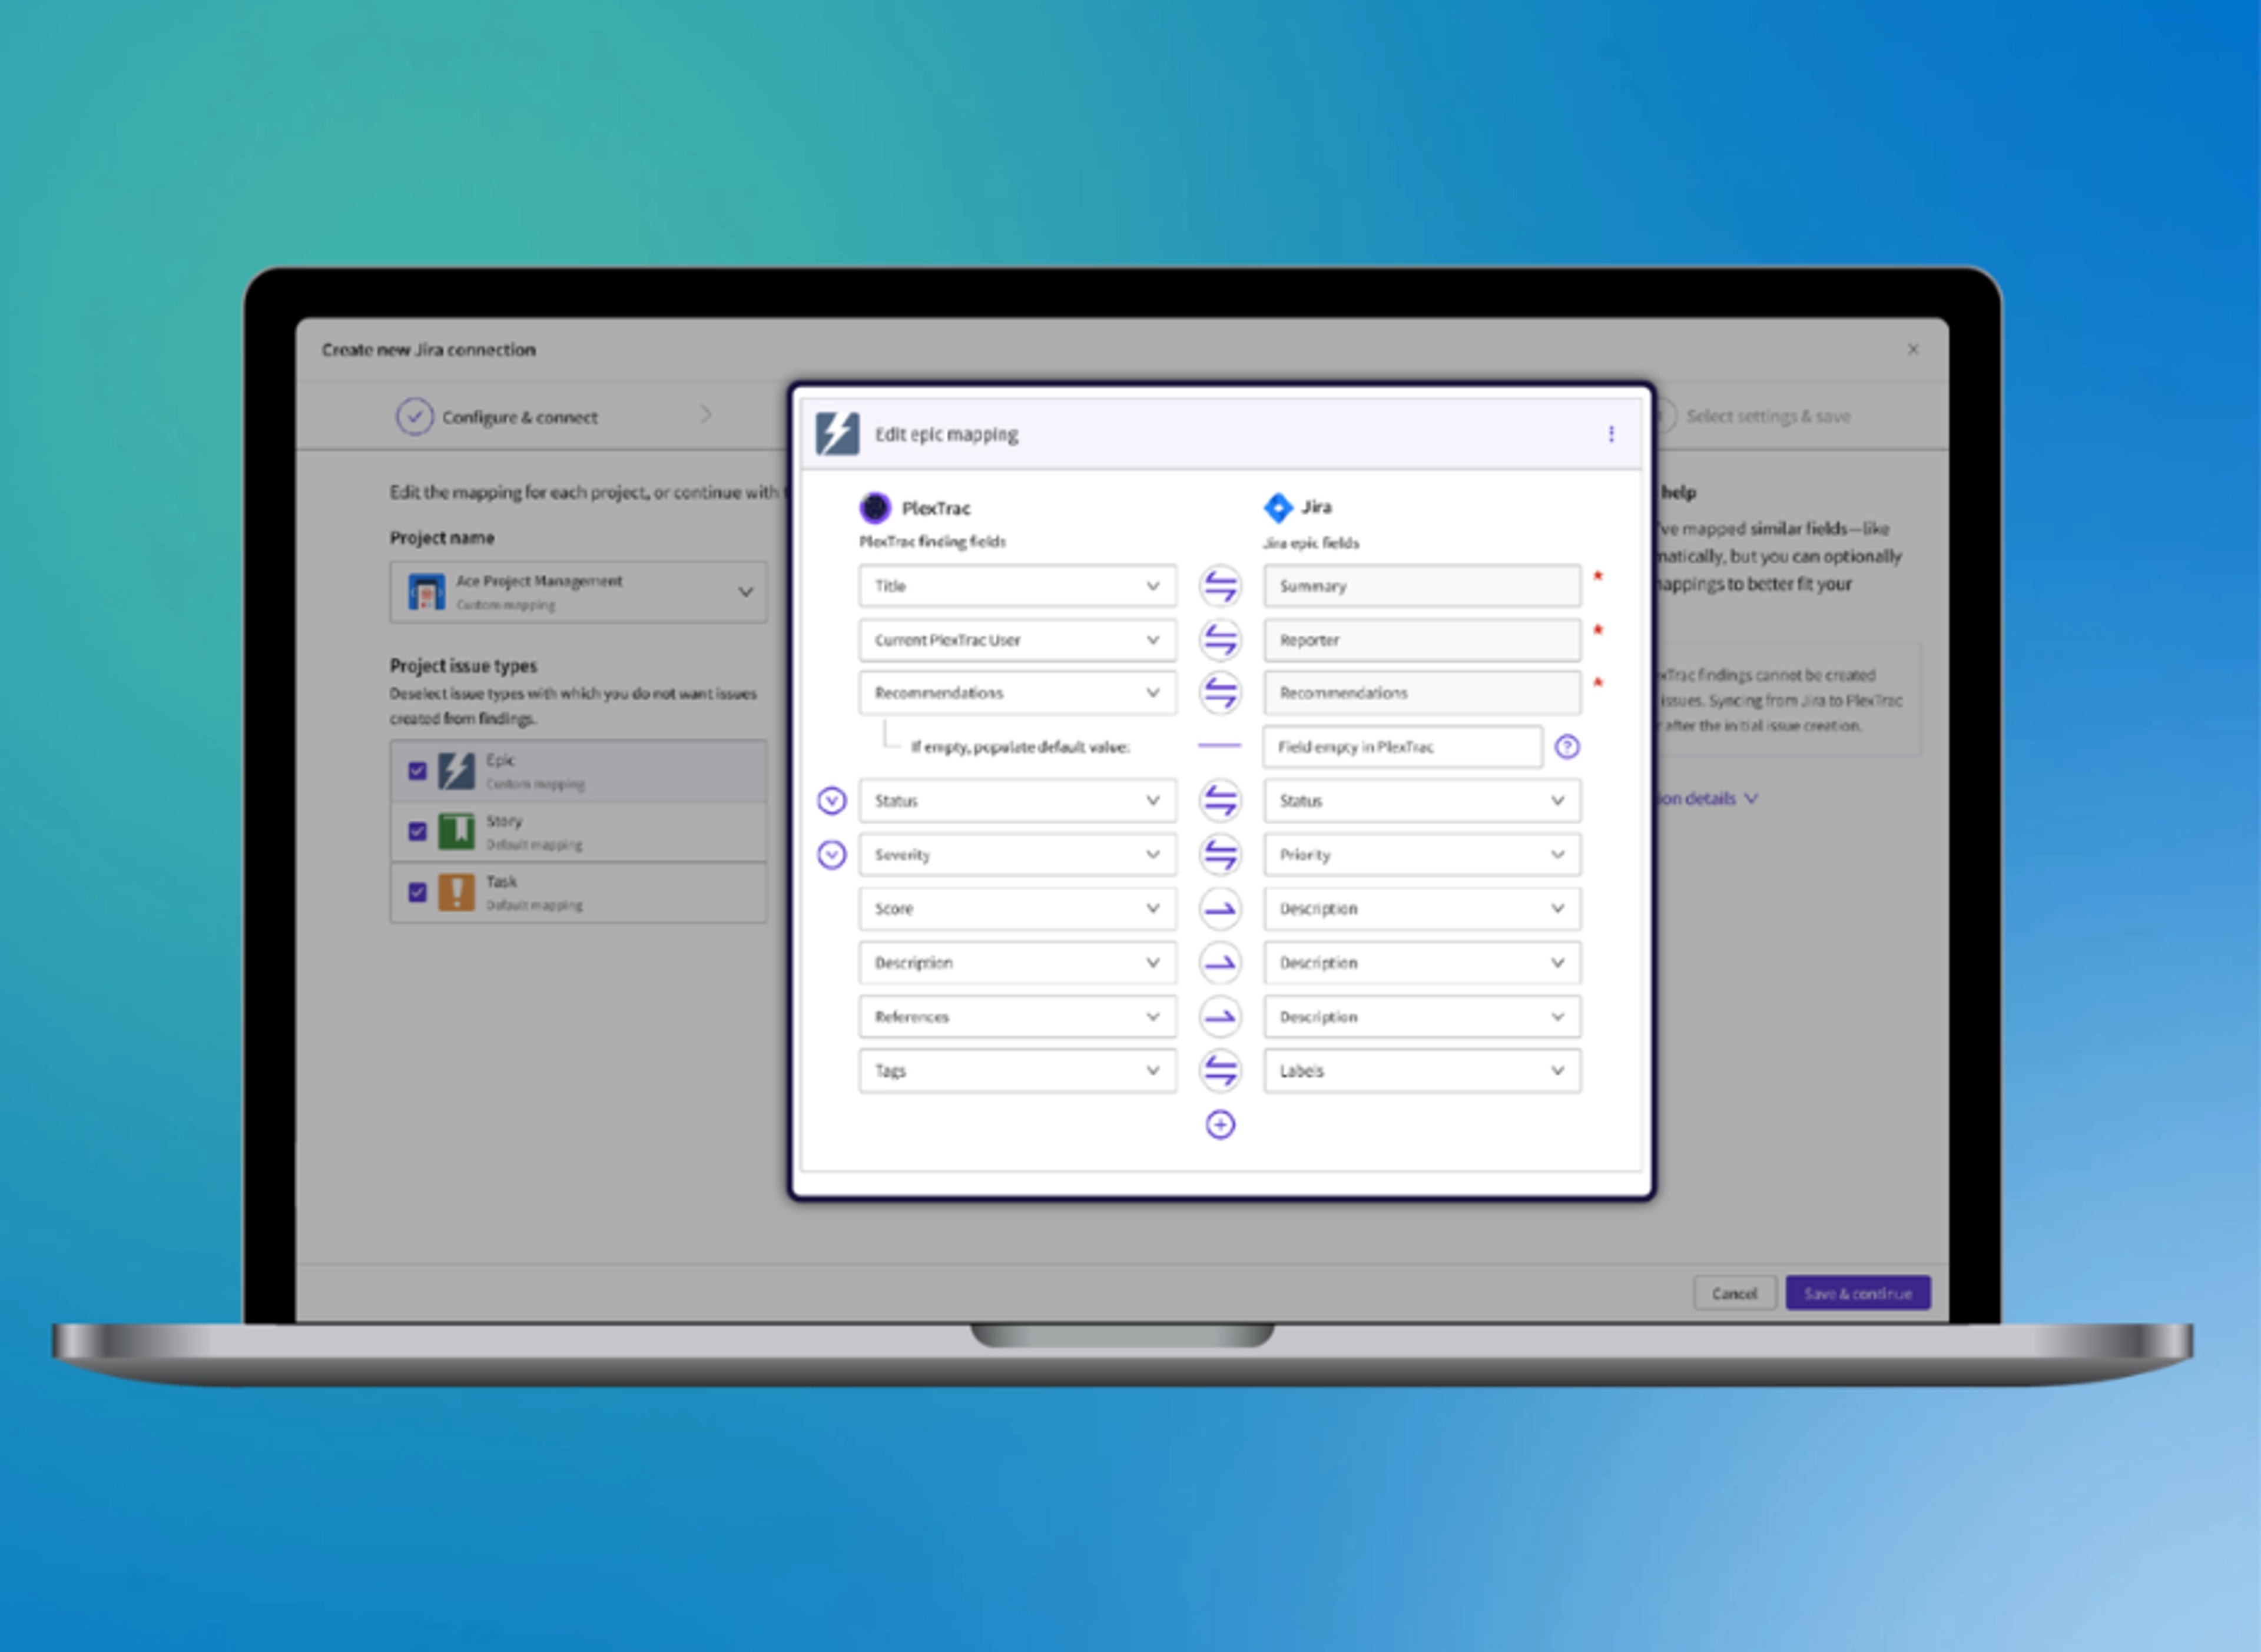
Hand off findings automatically
Bi-directional Jira and ServiceNow integrations move validated findings straight into remediation.
✓ Problems solved:
- Manual handoff to remediation. Validated findings flow into Jira and ServiceNow without being copied or retyped.
- Findings that slip through. Bi-directional sync keeps remediation status current, so every finding stays tracked.
"PlexTrac saves our team of 5 about 250 hours a year of work. You can do the math on pen testers at least costing $500 an hour, and so PlexTrac has a 5x ROI in year 1. "
– Verified PlexTrac User
Proven Customer Outcomes
Shorter reporting cycles and a return in the first year

30% Increase in efficiency

25K+ CVE, CWE & KEV findings write-ups

5X ROI in year one
What Brinqa adds
Take validated findings further with the Brinqa platform

The Brinqa CyberRisk Graph™
300+ connectors unifying every scanner, cloud and app security tool, and asset and identity source in your environment.

A ready-built PlexTrac connector
One of those 300+ connects directly to PlexTrac, so your validated findings and retest evidence flow into the Brinqa Cyber Risk Graph and inform every exposure management decision, no custom integration required.

Validated-exploitability prioritization
Your evidence-backed findings outweigh a scanner alert with the same score and no proof behind it.

AI Attribution and Deduplication
Ownership gaps close and duplicate findings disappear before prioritization runs.

SmartFlows automation
No-code workflows connecting security, IT, and offensive-testing teams end to end.

Who it's for
Built for every team that relies on offensive-security results.
Security Leaders
Show the board validated risk reduction, backed by retest evidence instead of a status update, and explain cyber risk in the business terms stakeholders understand.
Vulnerability and exposure management teams
Bring scanner, pentest and bug bounty findings into one view, assign clear ownership, and produce the remediation evidence auditors and regulators ask for.
Offensive security teams
Spend more time testing and less time formatting reports or chasing retest status, and give leadership defensible proof that findings get fixed.
For offensive security service providers
MSSPs: Turn Pen Test Reporting Into a Competitive Advantage
For offensive security service providers
MSSPs: Turn Pen Test Reporting Into a Competitive Advantage
MSSPs and pentest firms use PlexTrac by Brinqa to cut the hours consultants spend writing and formatting reports, deliver findings through a white-labeled client portal, and grow one-time engagements into recurring services.
- Recover billable time. AI-assisted authoring and a reusable findings library cut reporting cycles by up to 75%.
- Give clients real-time visibility. A white-labeled portal shows findings and retest status as the work happens, ahead of the final report.
- Deliver consistent quality across every consultant. Shared style guides keep each report in the client's format, whoever ran the test.
- Grow recurring revenue. Retest workflows and ongoing visibility turn one-time engagements into continuous client relationships.
Know what to fix first, prove the fix held.
Watch: Brinqa and PlexTrac – exposure management backed by validated evidence
FAQs
PlexTrac by Brinqa sits above the offensive-testing ecosystem the same way Brinqa sits above the scanning ecosystem: pen testing tools, red team and adversary emulation platforms, and validation and retest evidence all flow into one system of record for the offensive-security lifecycle.
PlexTrac by Brinqa keeps your testing, reporting, and validation workflow exactly as it is.
A ready-built PlexTrac connector connects directly to PlexTrac, so your validated findings and retest evidence flow into the Brinqa CyberRisk Graph™ and inform every exposure management decision, no custom integration required.
With PlexTrac, Brinqa closes the CTEM loop. PlexTrac's offensive security practitioners run pre-remediation testing to confirm an exposure is exploitable and post-remediation retesting to confirm the fix held. Every confirmed exploit and fix flows into the CyberRisk Graph, sharpening every AI agent that acts on it.
Automated handoff to remediation via bi-directional Jira, Azure DevOps, and ServiceNow integrations. Webhooks can also be used to enable custom workflows for various in-platform event triggers.
Deploy your way: multitenant cloud, private instance, or on-premises via Docker, so data residency and control requirements aren't a blocker.
PlexTrac's own MCP interface exposes real-time pentest and validation context to a customer's LLM of choice, read-only by design, respecting platform roles and permissions.
No, you can use PlexTrac without the Brinqa Platform.