Vulnerability Prioritization: How to Find, Fix, and Verify
by Brad Hibbert, COO & CSO//
Security teams at large enterprises face an overwhelming volume of vulnerabilities across global infrastructure and hybrid environments. Not all of them carry the same risk, and treating them as if they do drains resources while the exposures that matter stay open. Prioritization is how teams decide where to start.
A ranked list is only part of the job, though. Teams need to find what matters, fix what matters, and verify it was fixed. In this guide, we break down what vulnerability prioritization means today, the signals and framework that matter most, and how it connects to the steps before and after it, so security teams can focus on the vulnerabilities that pose real risk and show that risk came down.
What Is Vulnerability Prioritization?
Vulnerability prioritization is the process of determining which vulnerabilities should be addressed first based on their potential impact on the organization. It goes beyond severity scores to account for exploitability, asset importance, threat activity, and business impact, so limited resources go to the vulnerabilities that pose the greatest actual risk.
Where Vulnerability Prioritization Fits in CTEM
Vulnerability prioritization is the third of the five stages in continuous threat exposure management (CTEM), Gartner’s framework for running exposure management as a continuous program. Each stage builds on the one before it:
- Scoping: decide which parts of the business the program covers.
- Discovery: find the assets and exposures within that scope.
- Prioritization: rank those exposures by real risk to the business. This guide covers this stage.
- Validation: test whether an exposure can be used and confirm that remediation worked.
- Mobilization: get the right teams to act on the results.
In plain terms, this is the path most security leaders describe: find what matters, fix what matters, and verify it was fixed. Scoping and discovery find the exposures, prioritization decides which ones matter, mobilization gets them fixed, and validation checks the result. Prioritization depends on the data discovery produces, because incomplete or duplicated findings produce rankings teams can’t trust. It also only pays off if the fixes happen and are confirmed. For the full framework, see The 5 Stages of CTEM.
Why Prioritization Matters for Large Enterprises
The volume keeps growing. From January 1 to October 23, 2026, about 86,300 CVEs were published, up from about 38,600 in the same period of 2025 and already well above the 2025 full-year total of about 48,000, according to CyberHire’s analysis of CVE Program data. For large enterprises managing thousands of assets across hybrid environments, the volume is overwhelming. Compounding the challenge, vulnerability data is fragmented, remediation teams are stretched thin, and audit expectations are rising.
Only a small fraction of vulnerabilities are ever exploited. Microsoft’s September 2026 Patch Tuesday brought 966 CVEs, a new all-time record, and two were confirmed under active attack. Both were rated Important rather than Critical, so a process that only escalates Critical flaws would have missed them (Brinqa Research’s September Patch Tuesday analysis).
Prioritization is how security leaders reduce exposure and keep teams working on the vulnerabilities that matter most. It is essential for reducing cyber risk, for demonstrating accountability to executives and regulators, and for keeping overstretched security and IT teams focused and effective.
Traditional Approaches (and Why They Fall Short)
Historically, security teams have used methods such as:
- CVSS Scores: Static severity ratings that lack context.
- Manual Triage: Resource-intensive and inconsistent.
- Vulnerability Prioritization Matrices: Simple scoring grids that often fail to scale.
These approaches can be helpful starting points but often miss critical dimensions like real-world exploitability and business relevance. At enterprise scale, the shortfalls compound: static scores don’t adapt to new threat intelligence, low-risk issues absorb remediation time meant for critical fixes, and stakeholders can’t see why work was prioritized, which makes resources harder to justify. The result is mounting vulnerability backlogs, wasted effort, and missed risk signals.
A Risk-Based Vulnerability Prioritization Framework
Modern security programs use a risk-based approach that contextualizes vulnerabilities across multiple dimensions:
- Asset Criticality: How important is the affected system to business operations?
- Threat Intelligence: Are threat actors actively exploiting this vulnerability in the wild?
- Exploitability Signals: Is there known exploit code? What’s the EPSS (Exploit Prediction Scoring System) score? How likely is exploitation in your environment?
- Business Context: Who owns the system? What data does it process? Is it tied to a revenue-generating function?
- Exposure Context: Is the asset exposed to the internet or only accessible internally?
- Security Controls: Are compensating controls in place to mitigate the risk?
- Test Results: Did a safe, approved test show the weakness can be used against this asset?
This framework enables enterprise teams to align vulnerability remediation efforts with the organization’s risk appetite and compliance requirements. Explore the full methodology in our risk-based vulnerability management guide.
How to Prioritize Vulnerabilities for Remediation: A Step-by-Step Approach
The steps below follow the full path, from finding what matters to fixing it and verifying the result.
Find what matters
- Consolidate Vulnerability Data: Unify findings across scanners, cloud platforms, asset inventories, CMDBs, and pen testing tools. Large enterprises often deal with fragmented data sources. Normalizing, deduplicating, and reconciling this data is essential to gain full visibility.
- Enrich With Context: Add business metadata, ownership, and environment details to each finding. For example, identifying whether an asset supports a customer-facing product line or internal HR system adds vital prioritization context.
- Incorporate Threat and Exploit Intelligence: Use feeds like CISA KEV, EPSS, and commercial intel sources to gauge real-world risk. For a deeper dive on these scoring systems, see our post on EPSS vs. CVSS. Then judge how likely each weakness is to be exploited in your environment, based on exploit availability and how exposed the asset is.
- Score Based on Risk: The big shift this year is added focus on exploitability. Out of this mountain of findings, which ones matter to you? Which are actually reachable and exploitable, with significant impact on the business? Prioritize the exploits that are reachable, exploitable, and have the greatest impact. For example, a flaw on an internet-facing payment server with a working exploit and a clear route to customer data should move ahead of a higher severity flaw on an isolated test system that nothing can reach. Use a dynamic, configurable scoring model that weights exploitability, reachability, exposure, and business impact. Enterprise teams may need different scoring logic by business unit or region.
- Review Security Controls: Evaluate whether existing controls, like endpoint detection, segmentation, or web application firewalls, meaningfully reduce risk. A vulnerability may be deprioritized if strong, layered controls already mitigate it.
- Test Priorities With Evidence: Before committing remediation time, test the highest ranked findings. A safe, approved test that tries common, well-known attack techniques shows whether a weakness can be used in your environment, and the result can raise or lower the score. Results reflect the techniques tested at that point in time, so they inform the ranking and do not replace judgment.
Fix what matters
- Estimate Remediation Effort: Factor in the time, complexity, and potential service disruption associated with fixing each vulnerability. For example, patching a business-critical database may require downtime coordination and QA validation.
- Use a Two-Step Remediation: Given the potential impact and velocity of threats, organizations are moving toward a two-step remediation. Step one reduces exposure right away with a compensating action, such as a firewall rule, segmentation change, or WAF update. Step two applies the permanent fix on the normal patch schedule. The most exposed systems get protection in hours instead of waiting for a patch window.
- Automate Remediation Workflows: Trigger automated ticketing with SLAs, owner assignment, and escalation across IT, DevOps, and AppSec teams. Learn more in our post on automated vulnerability remediation. This reduces reliance on email or spreadsheets and ensures accountability.
Verify it was fixed
- Verify the Fix: A closed ticket does not confirm a closed exposure. After remediation, run the same tests again and rescan to check that the fix worked. Keep the evidence with the finding so owners, auditors, and executives can see what was tried and what happened.
- Measure and Refine: Track MTTR, SLA adherence, and false positive rates. Use dashboards to review backlog trends, team performance, and logic effectiveness. Continuously optimize for scale and accuracy.
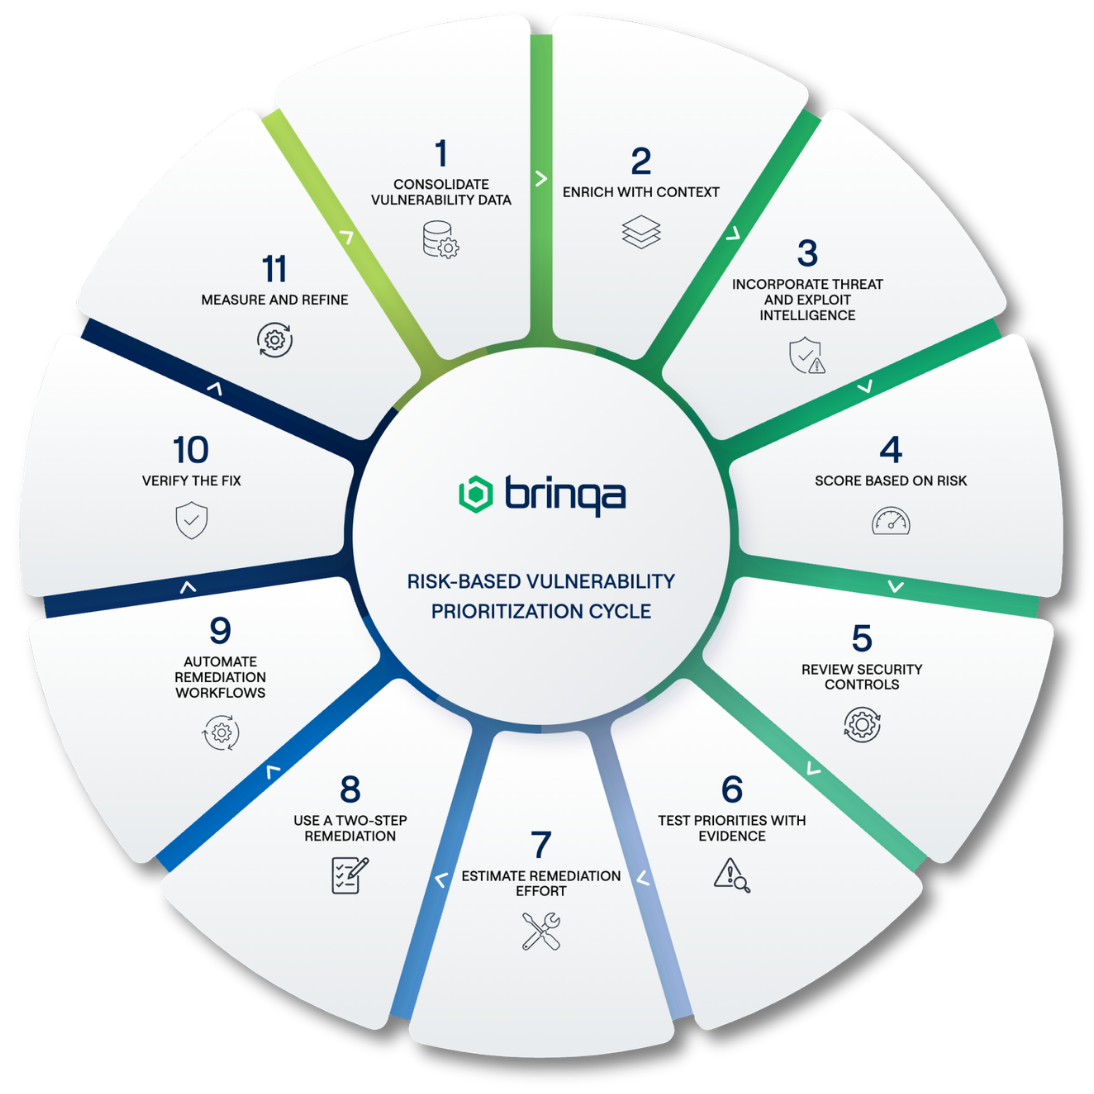
This eleven-step framework helps enterprise security teams find what matters, fix what matters, and verify the result at scale. The results are measurable: customers like Nestlé now identify critical vulnerabilities more than three times faster for same-day patching.
Aligning Remediation With Business Objectives
Prioritization isn’t just about technical severity. It must reflect how vulnerabilities affect the business. Aligning remediation to real risk and business impact helps ensure security efforts drive outcomes executives care about.
Examples of business-aligned prioritization:
- Prioritize vulnerabilities on systems tied to revenue, regulatory compliance, or customer trust (e.g., payment platforms, data warehouses, healthcare apps).
- Deprioritize issues on decommissioned systems, developer sandboxes, or assets isolated by design.
- Balance urgency against remediation effort, availability requirements, and stakeholder coordination.
When prioritization reflects enterprise business goals, it’s easier to justify remediation work, meet audit expectations, and foster trust between security and business teams.
Sample Vulnerability Prioritization Logic Table
| Condition | Priority Level |
|---|---|
Critical asset + known exploit | High |
Internet-facing + high EPSS score | High |
CVE participates in a known attack chain | High |
CVE appears to be reachable and exploitable | High |
Safe test succeeded using common attack techniques | High |
End-of-life software with no patch | Medium |
Internal-only + low impact + no known exploit | Low |
Fix applied, but retest still succeeds | Reopen the finding |
Enterprise Challenges in Vulnerability Prioritization
Managing vulnerability prioritization at scale introduces unique challenges, and frontier AI models have added new ones:
- High Volume and Velocity: The number of new vulnerabilities grows year over year. Teams struggle to triage issues quickly enough.
- Siloed Operations: Coordination between security, IT, cloud, and development teams is often fragmented.
- Resource Constraints: Many teams are understaffed or rely on manual processes that don’t scale.
- Visibility Gaps: Without full visibility into asset inventories and business context, prioritization logic breaks down.
- Accountability Pressure: Regulatory scrutiny and board-level reporting create added urgency and risk if prioritization fails.
- Closing the Loop: Many programs stop when a ticket closes. Without a retest, nobody knows whether the exposure is actually gone, and auditors ask for exactly that.
- AI-Accelerated Discovery: Frontier AI models now find vulnerabilities at a scale that previously required elite researchers, and vendors have built AI discovery into their own pipelines.
- Exploited Elsewhere, Not Always Exploitable Here: A weakness used in the wild may not be reachable or usable in your environment. Teams need a way to tell the difference.
- Trusting AI-Driven Decisions: “The AI said so” won’t satisfy a business owner or an auditor. AI recommendations need to show their reasoning, the controls in place, and the options available. They also need to be grounded in complete, live exposure data, with human review wherever the model’s confidence is low.
Overcoming these challenges requires an integrated platform that can bring together people, data, and processes, with AI that teams can trust because it’s grounded in their own data.
How Brinqa Covers the Path
Brinqa covers each step of the path on one platform. We also keep working with customers to evolve and enable their programs. Most teams start where the pain is greatest, such as consolidating data or cutting duplicate tickets, and extend from there as the program matures.
| Stage | What teams need | How Brinqa helps |
|---|---|---|
Find what matters | Complete, consistent data and a ranking they can explain | Connects to your scanners, cloud platforms, and asset sources. The Deduplication Agent consolidates duplicate findings and the Attribution Agent fills in missing ownership and attributes. Configurable risk scoring and the Exploitability Agent rank by likelihood, with transparent rules and tuning. |
Test priorities | Evidence before work begins | The Validation Agent runs scoped, approved tests using common attack techniques and uses the result to adjust the risk score before remediation. |
Fix what matters | The right owner, a ticket, and a due date | Automated ticketing, SLAs, owner assignment, and escalation across IT, DevOps, and AppSec teams. |
Verify it was fixed | Proof the exposure is closed | The Validation Agent tries the same techniques again after the fix. A full audit record shows what was tested, when, and the outcome. Dashboards track MTTR and SLA adherence. |
Transforming Prioritization into Action with Brinqa
If you’re leading a vulnerability management program at a large enterprise, you know that scale, context, and coordination are everything. The Brinqa Platform gives security program leaders unified visibility, risk-based logic, and automated workflows that work across silos. The platform’s AI layer handles the data cleanup and clarity prioritization depends on, from filling in missing ownership to consolidating duplicate findings, and helps teams check priorities and fixes with evidence.
The platform also includes cross-team collaboration features, pre-built reporting templates for compliance frameworks like NIST 800-53 and PCI DSS, and tailored dashboards for executives and auditors.
With our unified vulnerability and exposure management platform, security teams can:
- Unify vulnerability, asset, and threat data across hybrid environments
- Apply configurable risk scoring logic tailored to enterprise priorities, with transparent rules and tuning
- Rank by how likely a weakness is to be exploited in their own environment
- Test priorities before remediation and verify fixes afterward, with a full audit record
- Automate ticketing, SLA workflows, and remediation processes
- Improve MTTR across thousands of assets with cross-functional collaboration
- Generate executive-ready reports and dashboards for audit and board visibility
Brinqa delivers a centralized, risk-based approach to vulnerability management that scales with your organization and adapts to your unique context. We keep working with customers to evolve and enable their programs, from the first consolidated view to evidence that risk came down.
See how Fortune 500 security teams use Brinqa to scale vulnerability remediation.
FAQs
Vulnerability prioritization is the process of deciding which vulnerabilities to fix first, based on exploitability, asset criticality, threat activity, and business impact rather than severity scores alone.
Vulnerability prioritization means ranking security flaws by real-world risk instead of severity score alone. It combines exploitability, asset criticality, and business context to decide what to fix first.
This works by pulling in signals beyond CVSS: whether an exploit exists in the wild, how exposed the affected asset is, and what that asset actually supports in the business. A critical CVSS score on an isolated test server matters less than a medium score on a system handling customer data.
Key factors in vulnerability prioritization:
- Exploit Prediction Scoring System (EPSS) data on real-world exploitation likelihood
- Asset criticality and business context
- Network exposure and reachability
- Compensating controls already in place
Prioritization is the third of CTEM’s five stages, after scoping and discovery and before validation and mobilization. It turns the exposures discovery finds into a ranked list based on exploitability, asset criticality, and business impact.
Find means locating exposures and ranking them by real risk. Fix means getting the right owner to act with a clear due date. Verify means confirming the fix worked, ideally with a retest, and keeping the evidence.
CVSS rates how severe a vulnerability is. EPSS estimates how likely it is to be exploited in the next 30 days. Using both, alongside asset and business context, separates severe-but-unlikely issues from the ones attackers are targeting.
It’s a model that weighs asset criticality, threat intelligence, exploitability, business context, exposure, existing controls, and test results to rank vulnerabilities by actual risk to the organization.
AI agents prepare the data prioritization depends on and add evidence to it. In Brinqa, the Attribution Agent fills in missing attributes and ownership, and the Deduplication Agent consolidates duplicate findings from multiple scanners, so risk scoring runs on complete, consistent records. The Exploitability Agent judges how likely each weakness is to be exploited in your environment, and the Validation Agent tests priorities and fixes using common attack techniques.
An attack chain is a series of steps an attacker links together, such as getting a foothold with one weakness, then moving to other systems and reaching something valuable. A CVE that appears in a chain matters more than its score suggests, because it opens the way for the steps that follow. Public sources describe chains seen in real attacks. MITRE ATT&CK maps attacker techniques and the groups that use them. The CISA Known Exploited Vulnerabilities catalog and CISA advisories list weaknesses attackers are using now, and many advisories walk through the full sequence. Vendor threat reports and incident write-ups add detail. Teams can bring these signals into their scoring so a CVE tied to a known chain ranks higher, then check whether the chain could work in their own environment.
Automated red teaming uses software to run attack techniques against your environment on demand or on a schedule, instead of waiting for an annual manual test. Validation applies the same idea to specific findings. It tries common techniques against a weakness to see whether it can be used, which can adjust the risk score before remediation, and it tests again after the fix to confirm the fix worked. Both show what was tried and what happened at that point in time.
As evidence from the techniques tested at that point in time. A test that succeeds is a strong reason to move a finding up. A test that does not succeed shows what was tried and what happened, and teams can run it again as their environment changes. Full audit details come with every result.
A vulnerability prioritization matrix is a simplified scoring grid that helps teams rank vulnerabilities based on severity and asset importance. While useful as a starting point, it often lacks the depth and scalability of a risk-based approach.
No, Brinqa integrates with your existing scanning tools. It provides the intelligence and workflows needed to make vulnerability data actionable.
By pairing the ranking with proof. Verifying each fix with a retest, keeping the evidence with the finding, and tracking MTTR and SLA adherence gives owners, auditors, and executives a record of what was tried and what happened. Executive-ready reports and dashboards then carry that record to the board.